Tenant separation
Every community works in its own logically separated data area.
Workspaces stay separate, permissions are tiered and relevant actions are logged in a traceable way.
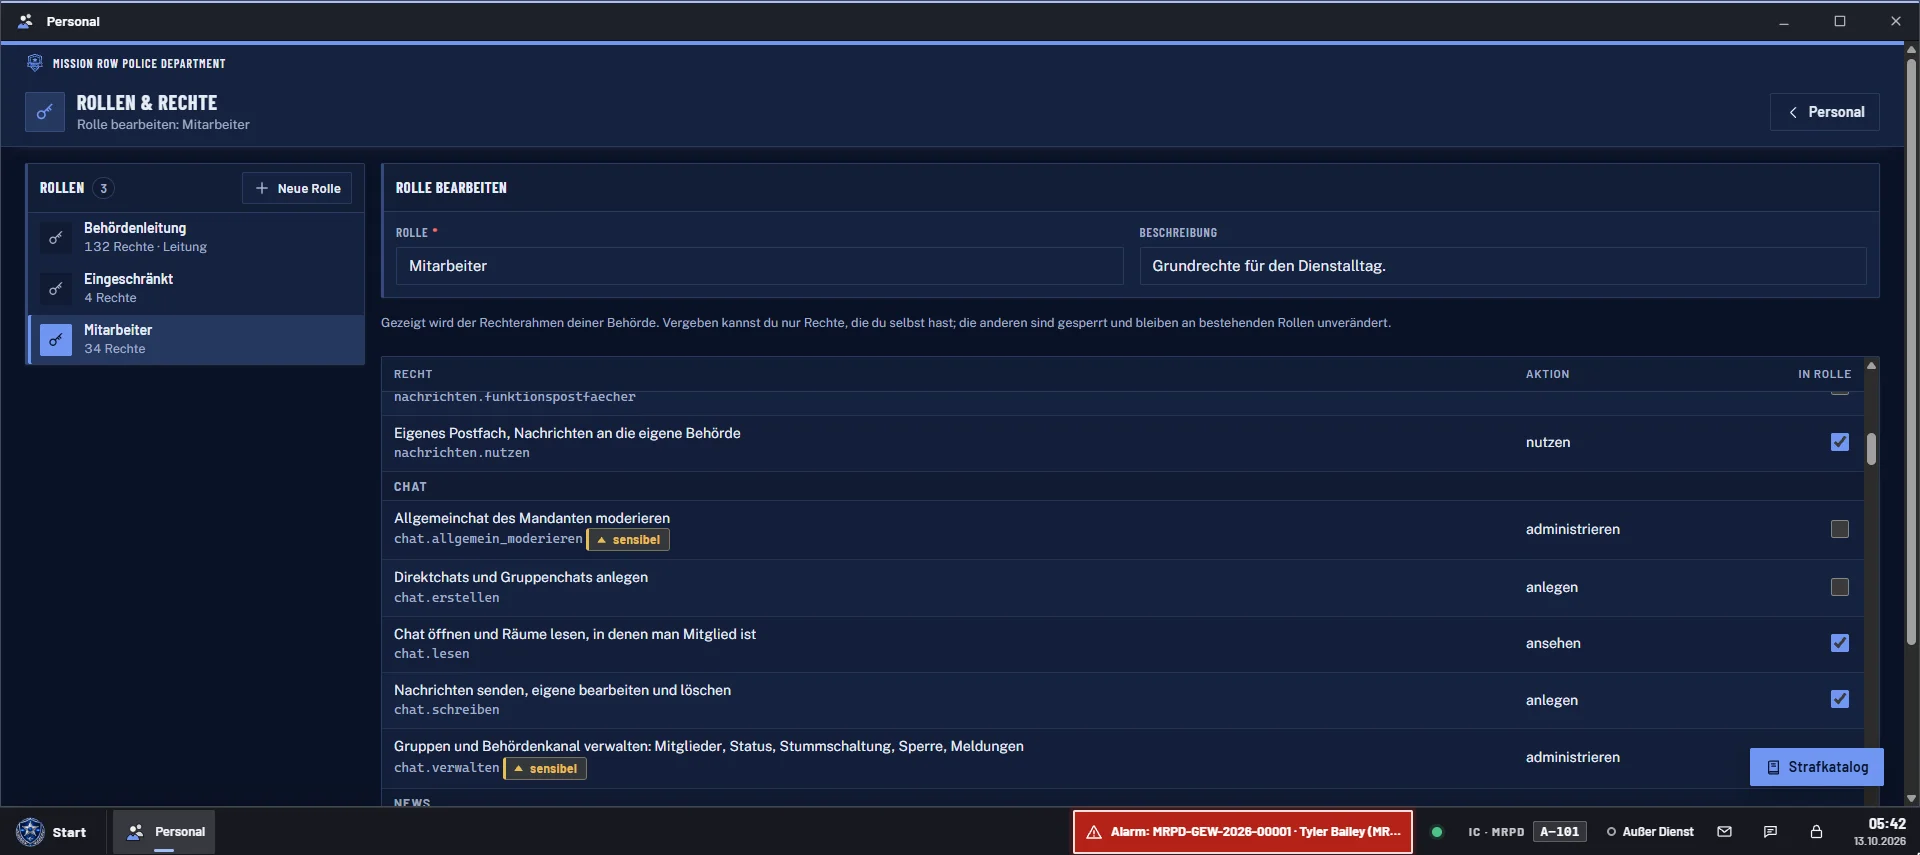
Every community works in its own logically separated data area.
Organization, rank and confidentiality determine access.
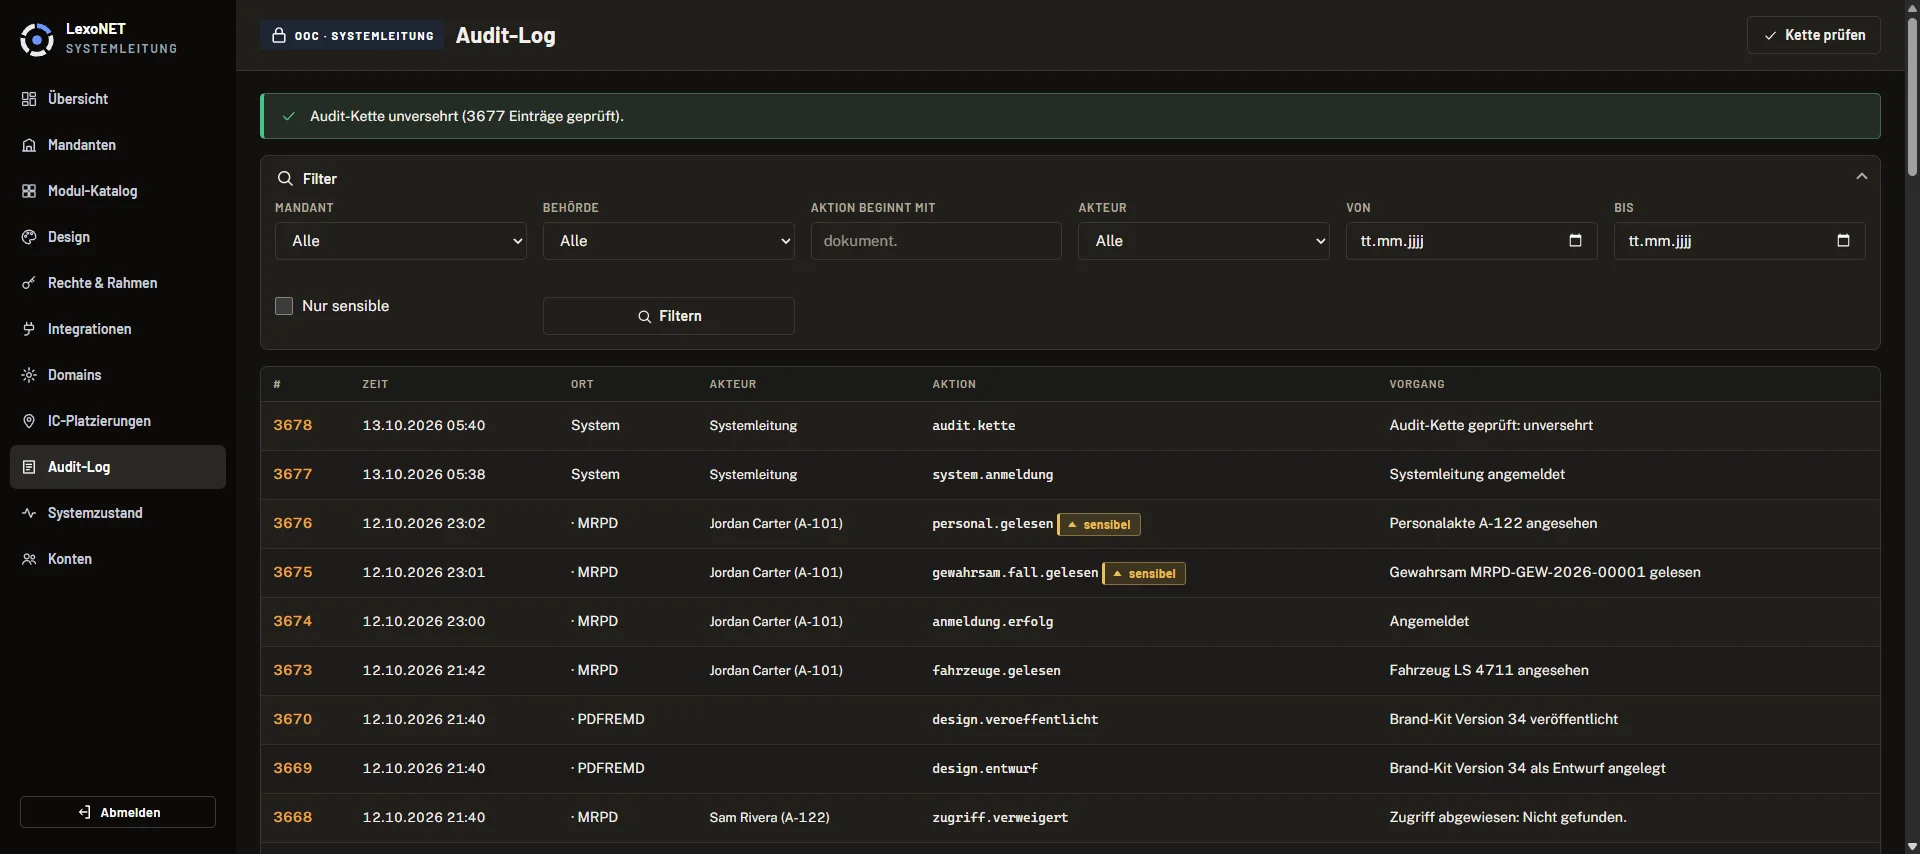
Access and changes remain traceable with timestamps. The log chain can be checked for tampering at any time.
Support access only happens after approval and is logged.
Penalties and DNA matches only take effect once a second authorized person approves.
Share records and BOLOs selectively, time-limited and revocable at any time.
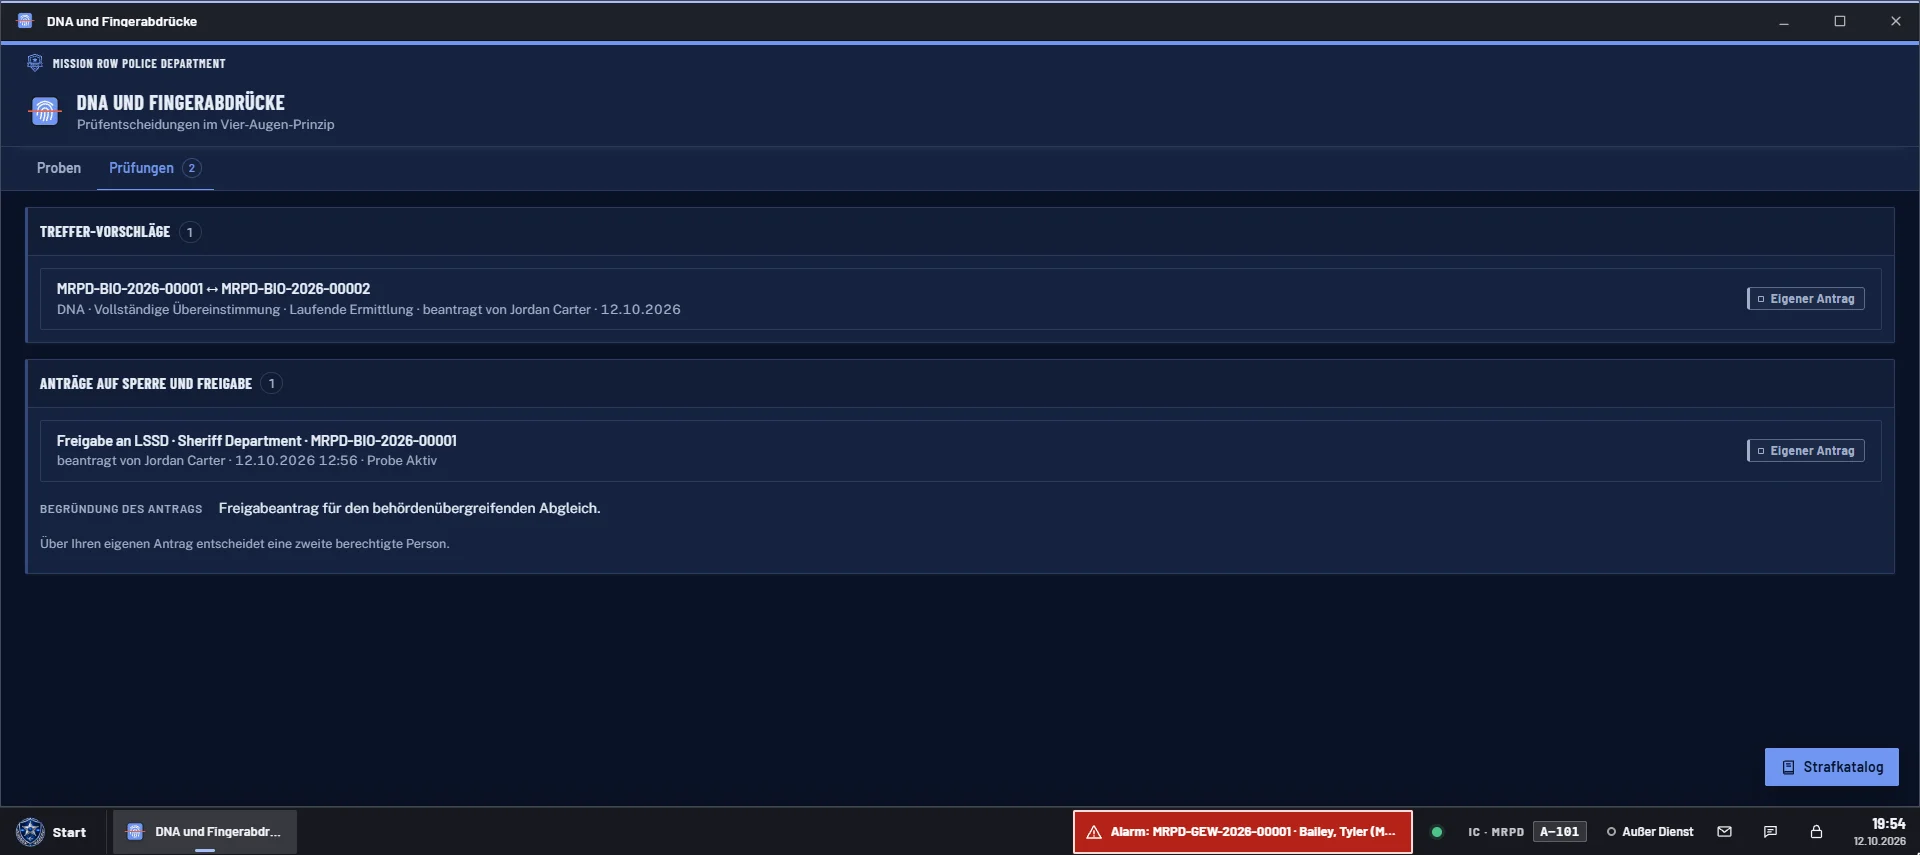
The four-eyes principle prevents critical decisions from becoming binding through a single person.
Approvals connect agencies only for the case at hand and can be time-limited or revoked.
